Ethereum client security fixes leave binary users with a separate Java check
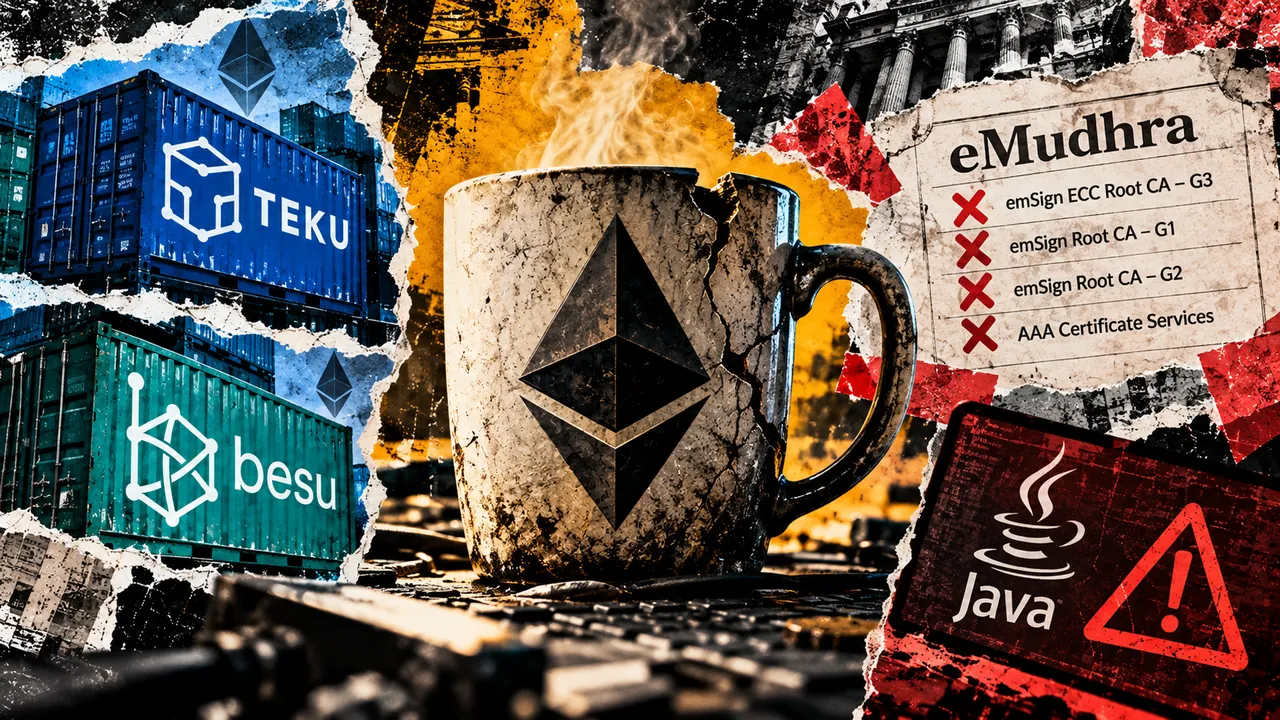
Image: CryptoSlate
Teku and Besu, software used to run Ethereum nodes, have shipped Docker security fixes after a certificate-authority compromise at eMudhra. Operators using affected images can update those containers. Binary installations need a separate check of their Java runtime. Teku 26.10.3 , released Oct. 27, and Besu 26.10.2 , released Oct. 26, stop their Docker images trusting four certificate roots: emSign ECC Root CA – G3, emSign Root CA – G1, emSign Root CA – G2 and AAA Certificate Services. For Teku, exposure depends on configuration. The team's security notice says default mainnet nodes without HTTPS URLs are unaffected. On an unremediated runtime, an attacker would need to intercept an affected HTTPS connection to impersonate its endpoint. The notice reports no exploitation.
Read the full story on CryptoSlateBeCrypto News shows a short excerpt and links to the publisher. The full report belongs to CryptoSlate.