Keystone Wallet Data Breach Exposes Buyers’ Addresses to Scammers
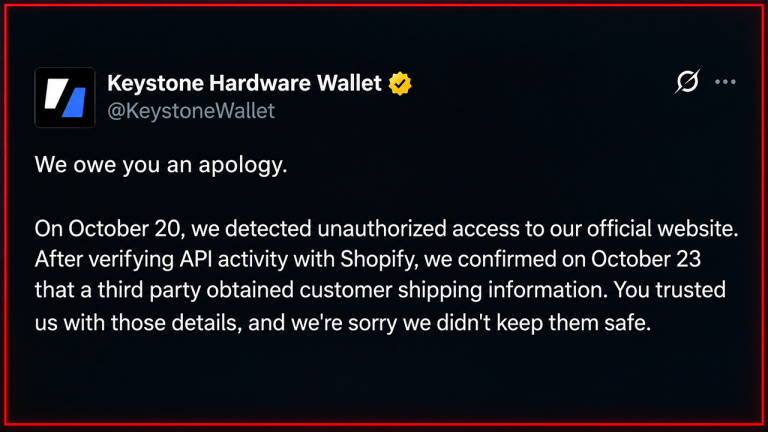
Image: Bitcoin.com News
Hardware wallet maker Keystone disclosed a customer data breach on Saturday, after unauthorized access to its website exposed names, shipping addresses, contact information and purchase details. The company says recovery phrases and private keys remain secure. The incident adds Keystone to a growing list of hardware wallet manufacturers facing security problems in 2026, including Ledger, Trezor, Safepal and Coldcard. A hardware wallet designed to keep cryptocurrency secrets offline has encountered a security problem somewhere entirely different: its online storefront. On Saturday, Keystone disclosed at 1:59 p.m. ET that an unauthorized party had obtained customer shipping information through its website, potentially giving scammers the personal details needed to impersonate the company.
Read the full story on Bitcoin.com NewsBeCrypto News shows a short excerpt and links to the publisher. The full report belongs to Bitcoin.com News.