Hackers found a way to steal Bitcoin without private keys
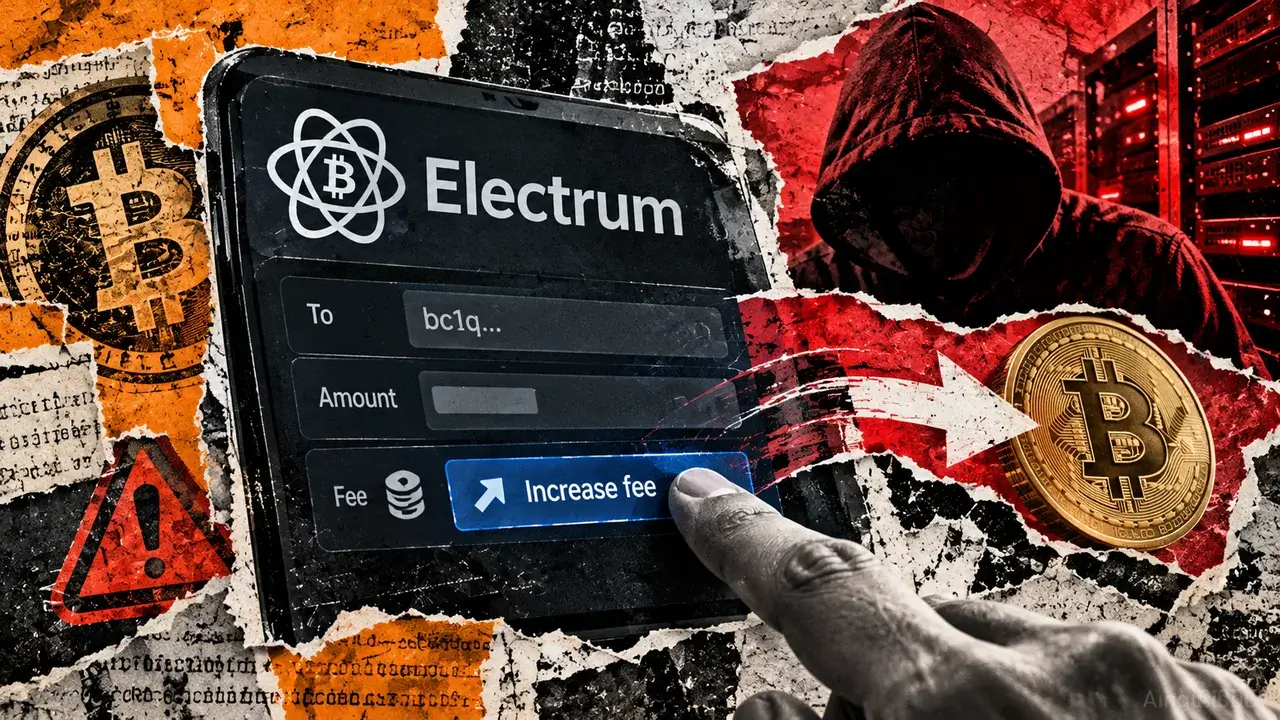
Image: CryptoSlate
Bitcoin wallet Electrum has patched a security flaw that allowed hackers to redirect payments when users tried to increase transaction fees. The developers disclosed the vulnerability on Oct. 24, confirming that malicious servers had exploited the weakness and that at least one user lost Bitcoin after unknowingly approving a fraudulent transaction. The high-severity vulnerability affects Electrum versions earlier than 4.8.3. It exploits the wallet's reliance on external servers to track unconfirmed transactions, allowing attackers to manipulate the payment information users see before they authorize additional fees. The disclosure followed two complaints received on Oct. 11 and Oct. 18. The first user noticed an unfamiliar transaction appearing in their wallet after broadcasting a payment, while the second reported losing funds after attempting to accelerate a pending transfer.
Read the full story on CryptoSlateBeCrypto News shows a short excerpt and links to the publisher. The full report belongs to CryptoSlate.