Cardano’s $0.19 defense: Who’s buying ADA and why it matters
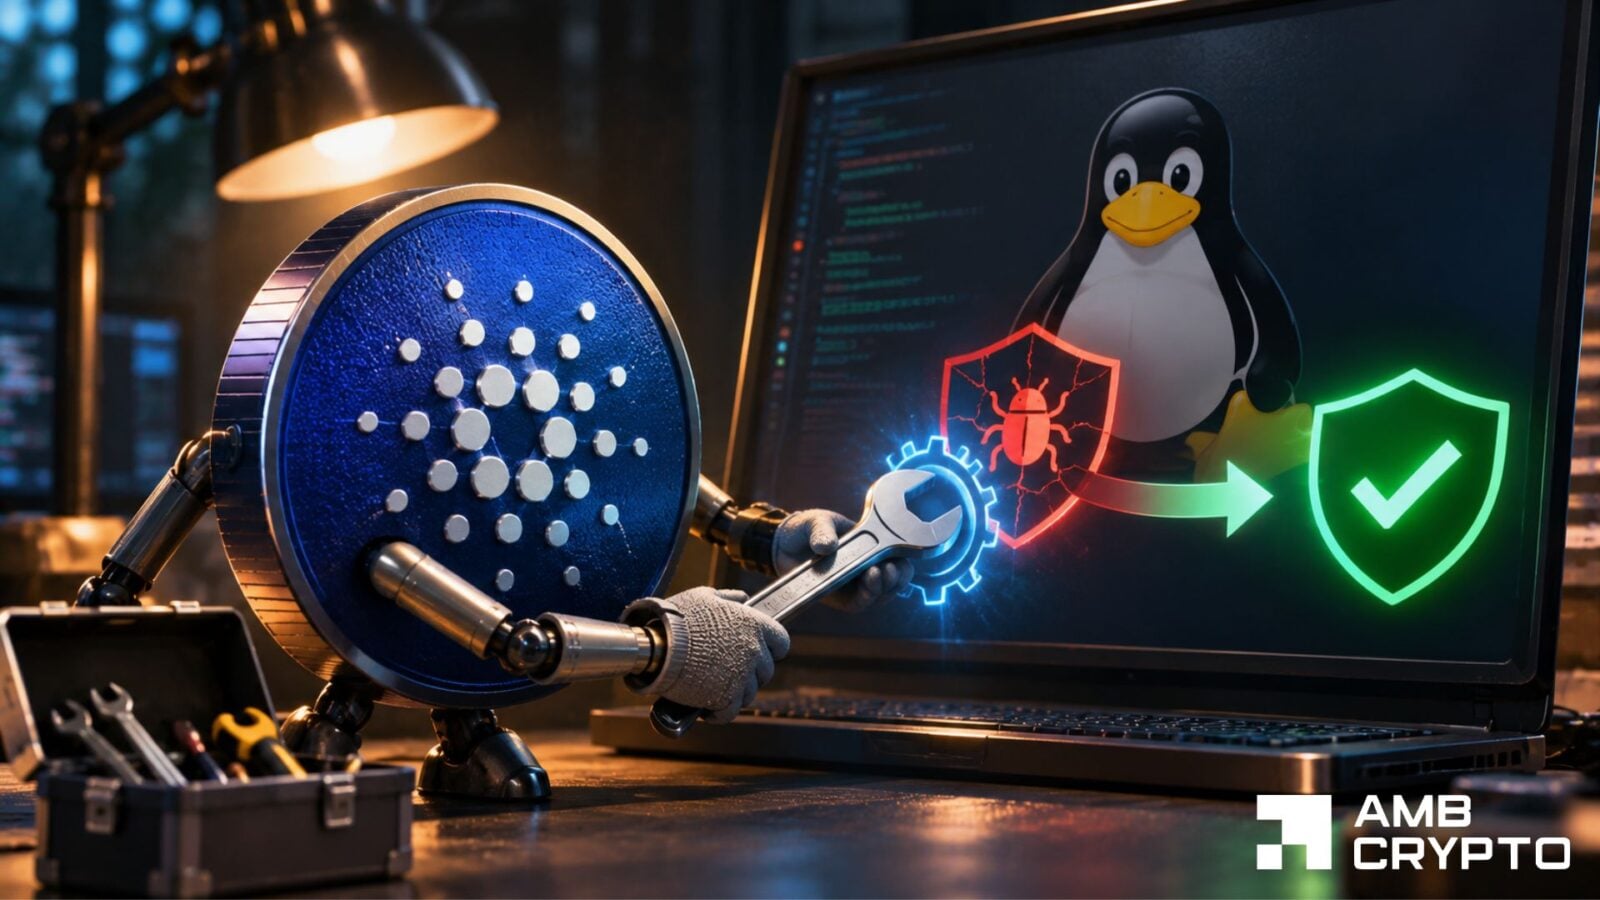
Image: AMBCrypto
Intersect, a Cardano ecosystem governance entity, has recommended that stake pool operators (SPOs) upgrade their systems to patch a critical Linux flaw. The vulnerability, tracked as CVE-2026-98432, could allow an attacker to inject and execute a remote malicious code remotely. According to Red Hat’s security brief, the flaw has a CVSS severity score of 9.8 and system-wide scope across major Linux systems, including Ubuntu, which powers Cardano. The flaw is within the Linux kernel subsystem that handles internet connections ( IPv4 TCP connections). It can allow an attacker to exploit a node (block producer) or relay, effectively leading to node crashes or data corruption. So far, some Linux systems have been fixed with relevant patches.
Read the full story on AMBCryptoBeCrypto News shows a short excerpt and links to the publisher. The full report belongs to AMBCrypto.